- 01Finding lifecycle API
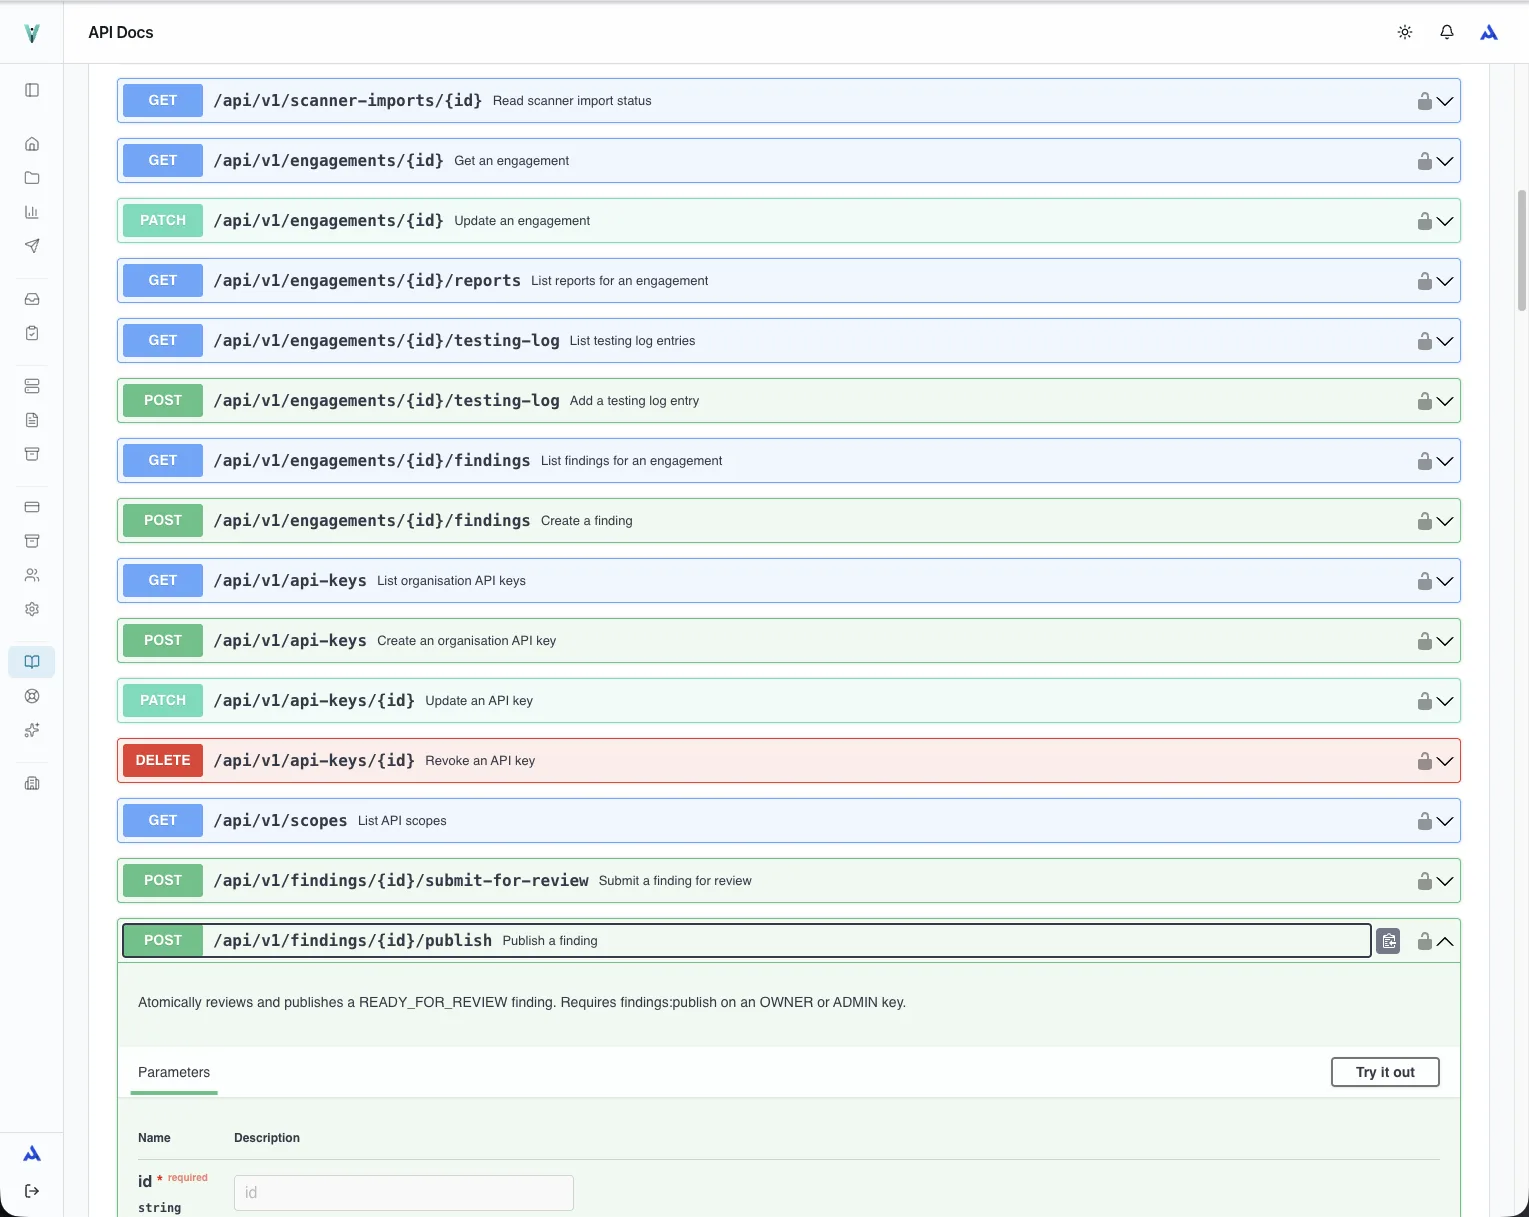
- Create, review, publish, remediate, retest, and audit findings through documented state-aware operations with consistent structured errors.
- 02Recon and asset history
- Discover and verify live hosts, bring selected targets into scope, and keep finding history attached to the same asset across engagements.
- 03Methodology and proof of work
- Track pass, fail, not-applicable, and not-tested outcomes; keep the raw operator log internally while automatically redacting recognized credential values in client-facing reports.
- 04Remediation SLAs and retests
- Start severity-based deadlines when a finding is published, record passed or failed retests, surface overdue work, and retain the full transition history.
- 05Controlled web delivery
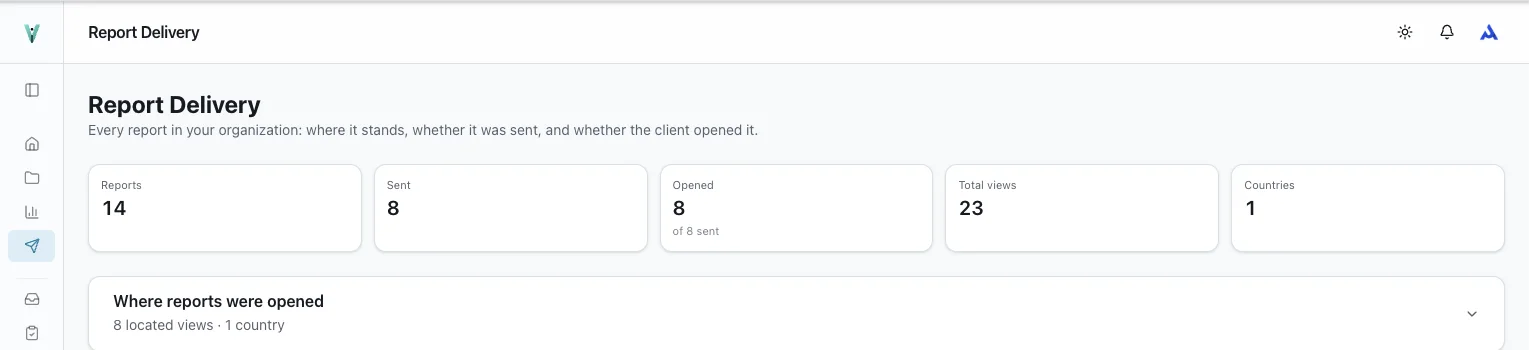
- Share read-only reports through revocable links with optional passphrases and a visit-by-visit access log.
- 06Portfolio visibility and intake
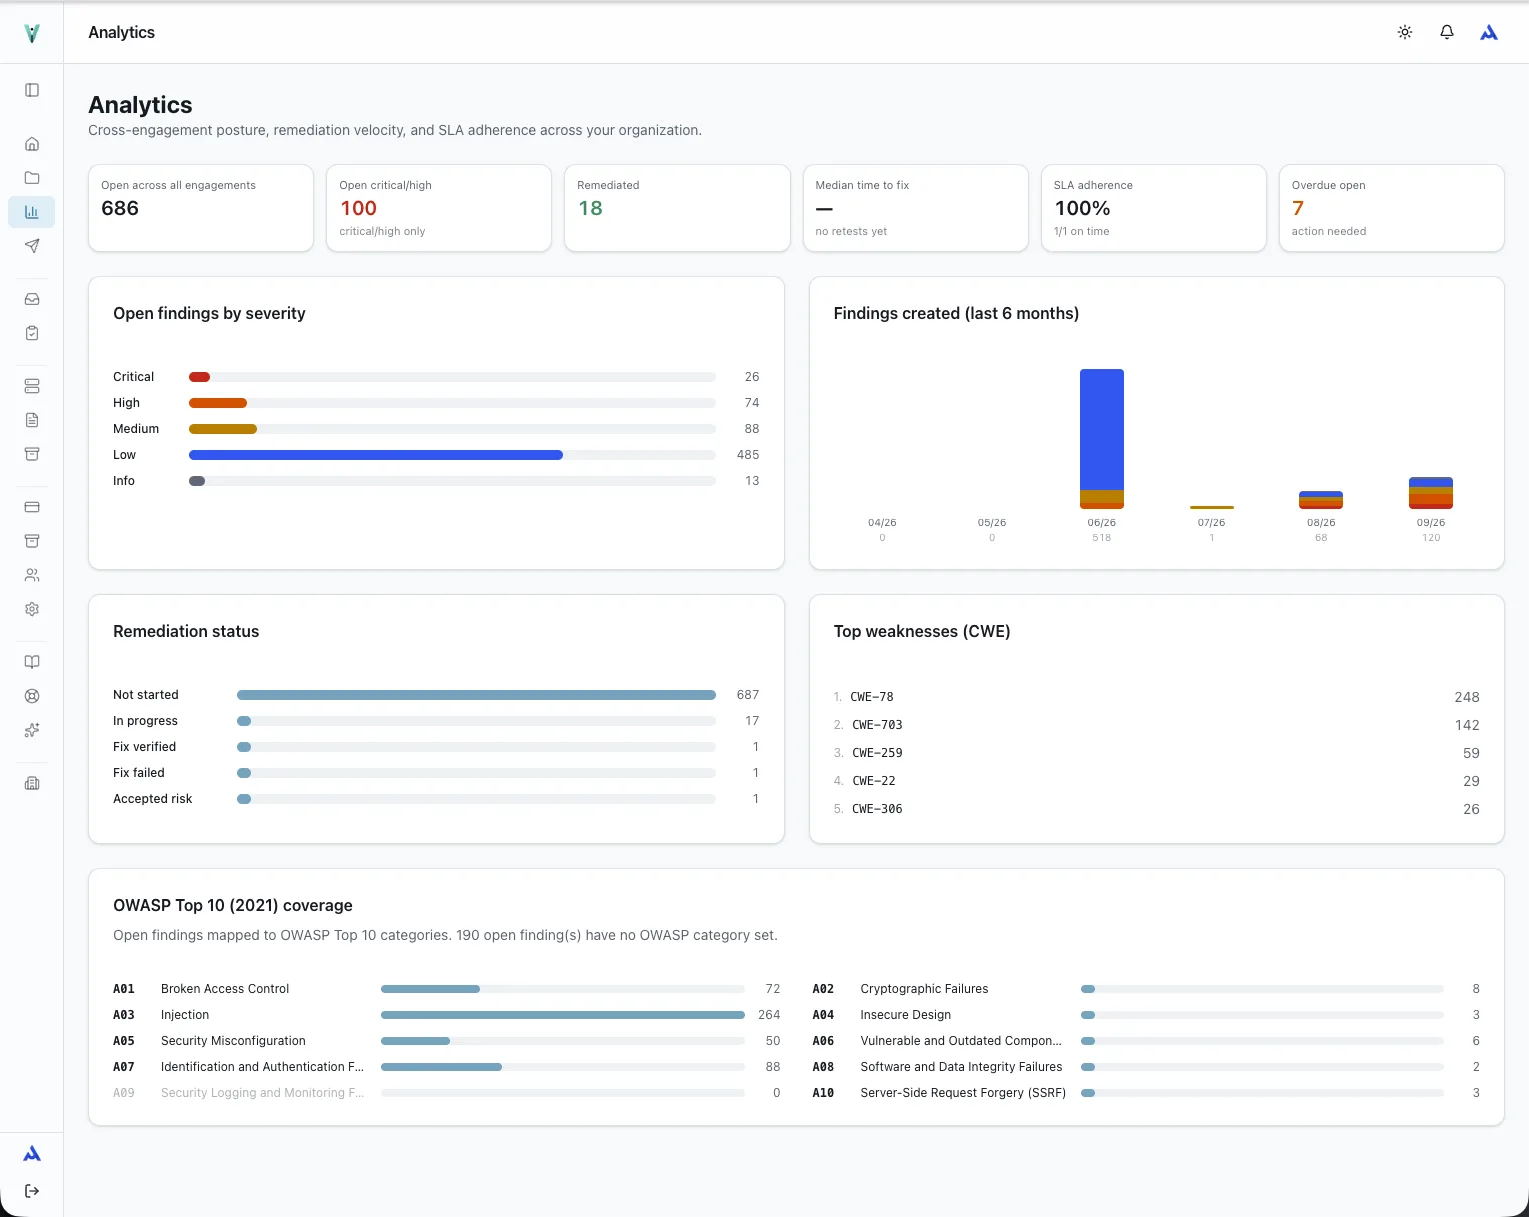
- Measure open risk, time to fix, SLA adherence, recurring weaknesses, and OWASP coverage; turn an approved client request into a planning engagement.